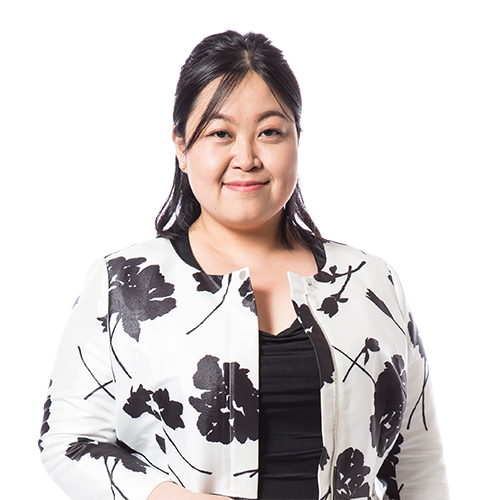
On September 28, Wang Fei, a senior partner at Beijing King&Capital Law Firm, was invited to conduct a special training session titled “Legal Pathways and Risk Management for Unlocking the Value of Data Elements in the Red Cross” for the Chinese Red Cross Society.
The Red Cross system has accumulated a vast amount of data through its humanitarian operations, including volunteer services, first aid training, relief donations, and organ donation services. This data contains a significant amount of sensitive personal information, and the sharing and circulation of such data directly impact the organization’s public trust. Balancing the unlocking of data value with the protection of personal information and data security—and translating compliance requirements into practical, traceable management measures—is a critical practical challenge in the Red Cross’s digital transformation process.
This training focused on three core issues: data value extraction, legal arrangements for cross-system data flow, and the implementation of rights and responsibilities regarding data sharing. Drawing on the *Cybersecurity Law*, the *Data Security Law*, the *Personal Information Protection Law*, and numerous typical judicial and law enforcement cases, Attorney Wang Fei explained the three legal pathways for data sharing within the Red Cross system and the three-step compliance assessment criteria, with a focus on preventing various risks that may arise during business operations—such as exceeding authorized access, excessive disclosure of privacy, and inadequate oversight of third-party operations and maintenance.
The session placed particular emphasis on field-level data inventory management. Ms. Wang distinguished between four types of legal relationships—data sharing, entrusted processing, joint processing, and query access—clarifying the rights and responsibilities of all parties. She emphasized that under an entrusted processing model, service providers must not retain or subcontract data without authorization, and that data must be deleted or returned upon project termination. She also proposed that data-sharing agreements should be detailed down to the field level to clearly delineate the boundaries of data usage.
Addressing the boundary between public interest disclosure and privacy protection, she explicitly stated during the training that the public interest nature of an organization does not exempt it from its obligation to protect personal information; sensitive information must undergo de-identification before the disclosure of relief and donation information. During the course, Attorney Wang Fei established four practical guidelines: statistical results take precedence over individual details; de-identified data takes precedence over raw data; and interface verification takes precedence over bulk exports. She also outlined six lines of defense for risk governance: systems, checklists, authorizations, technology, contracts, and oversight.
Addressing common practical issues such as business reporting, integration with multiple systems, and service providers’ use of real data for debugging, she provided clear operational guidelines. She noted that debugging with real business data constitutes a controlled exception that must undergo approval, restrict authorized users and duration, maintain a complete audit trail throughout the process, and ensure data is permanently deleted upon completion.
Attorney Wang Fei pointed out that unlocking the value of Red Cross data is not synonymous with simply opening up data, nor does risk governance mean restricting data use. Instead, it should ensure clear data sources, well-defined purposes, controllable access permissions, and traceable accountability, embedding compliance requirements throughout the entire business process to empower the high-quality development of the Red Cross cause through security and compliance.